How I scaled GRC
Automation first.
Headcount last.
When I started, there was no SOC 2, no policies, no vendor risk assessments and no risk management. I’m still the only person running GRC, so I treated it as an engineering problem: build each process once, then automate it.
Where I startedThe business needed SOC 2. There was no program.No SOC 2, no policies, no vendor risk assessments, no risk management. Everything on this page started from zero.
What I builtThree frameworks, 119 controls, one platform.Drata set up from scratch with every integration built myself. SOC 2 and PCI DSS v4 run side by side with no duplicate work, plus an ISO 42001 gap analysis for AI.
What it changedA clean first SOC 2 Type 2. No findings.Automation cut manual compliance effort by over 60%. That’s how I, still the only person in GRC, run SOC 2, PCI DSS, AI governance, vendor risk, risk management and policy.
01Map once, comply manyOne control set mapped across SOC 2 and PCI DSS, so each control is evidenced once.
02Automate the evidenceEligible controls evidenced and monitored automatically, with failures sent to Slack.
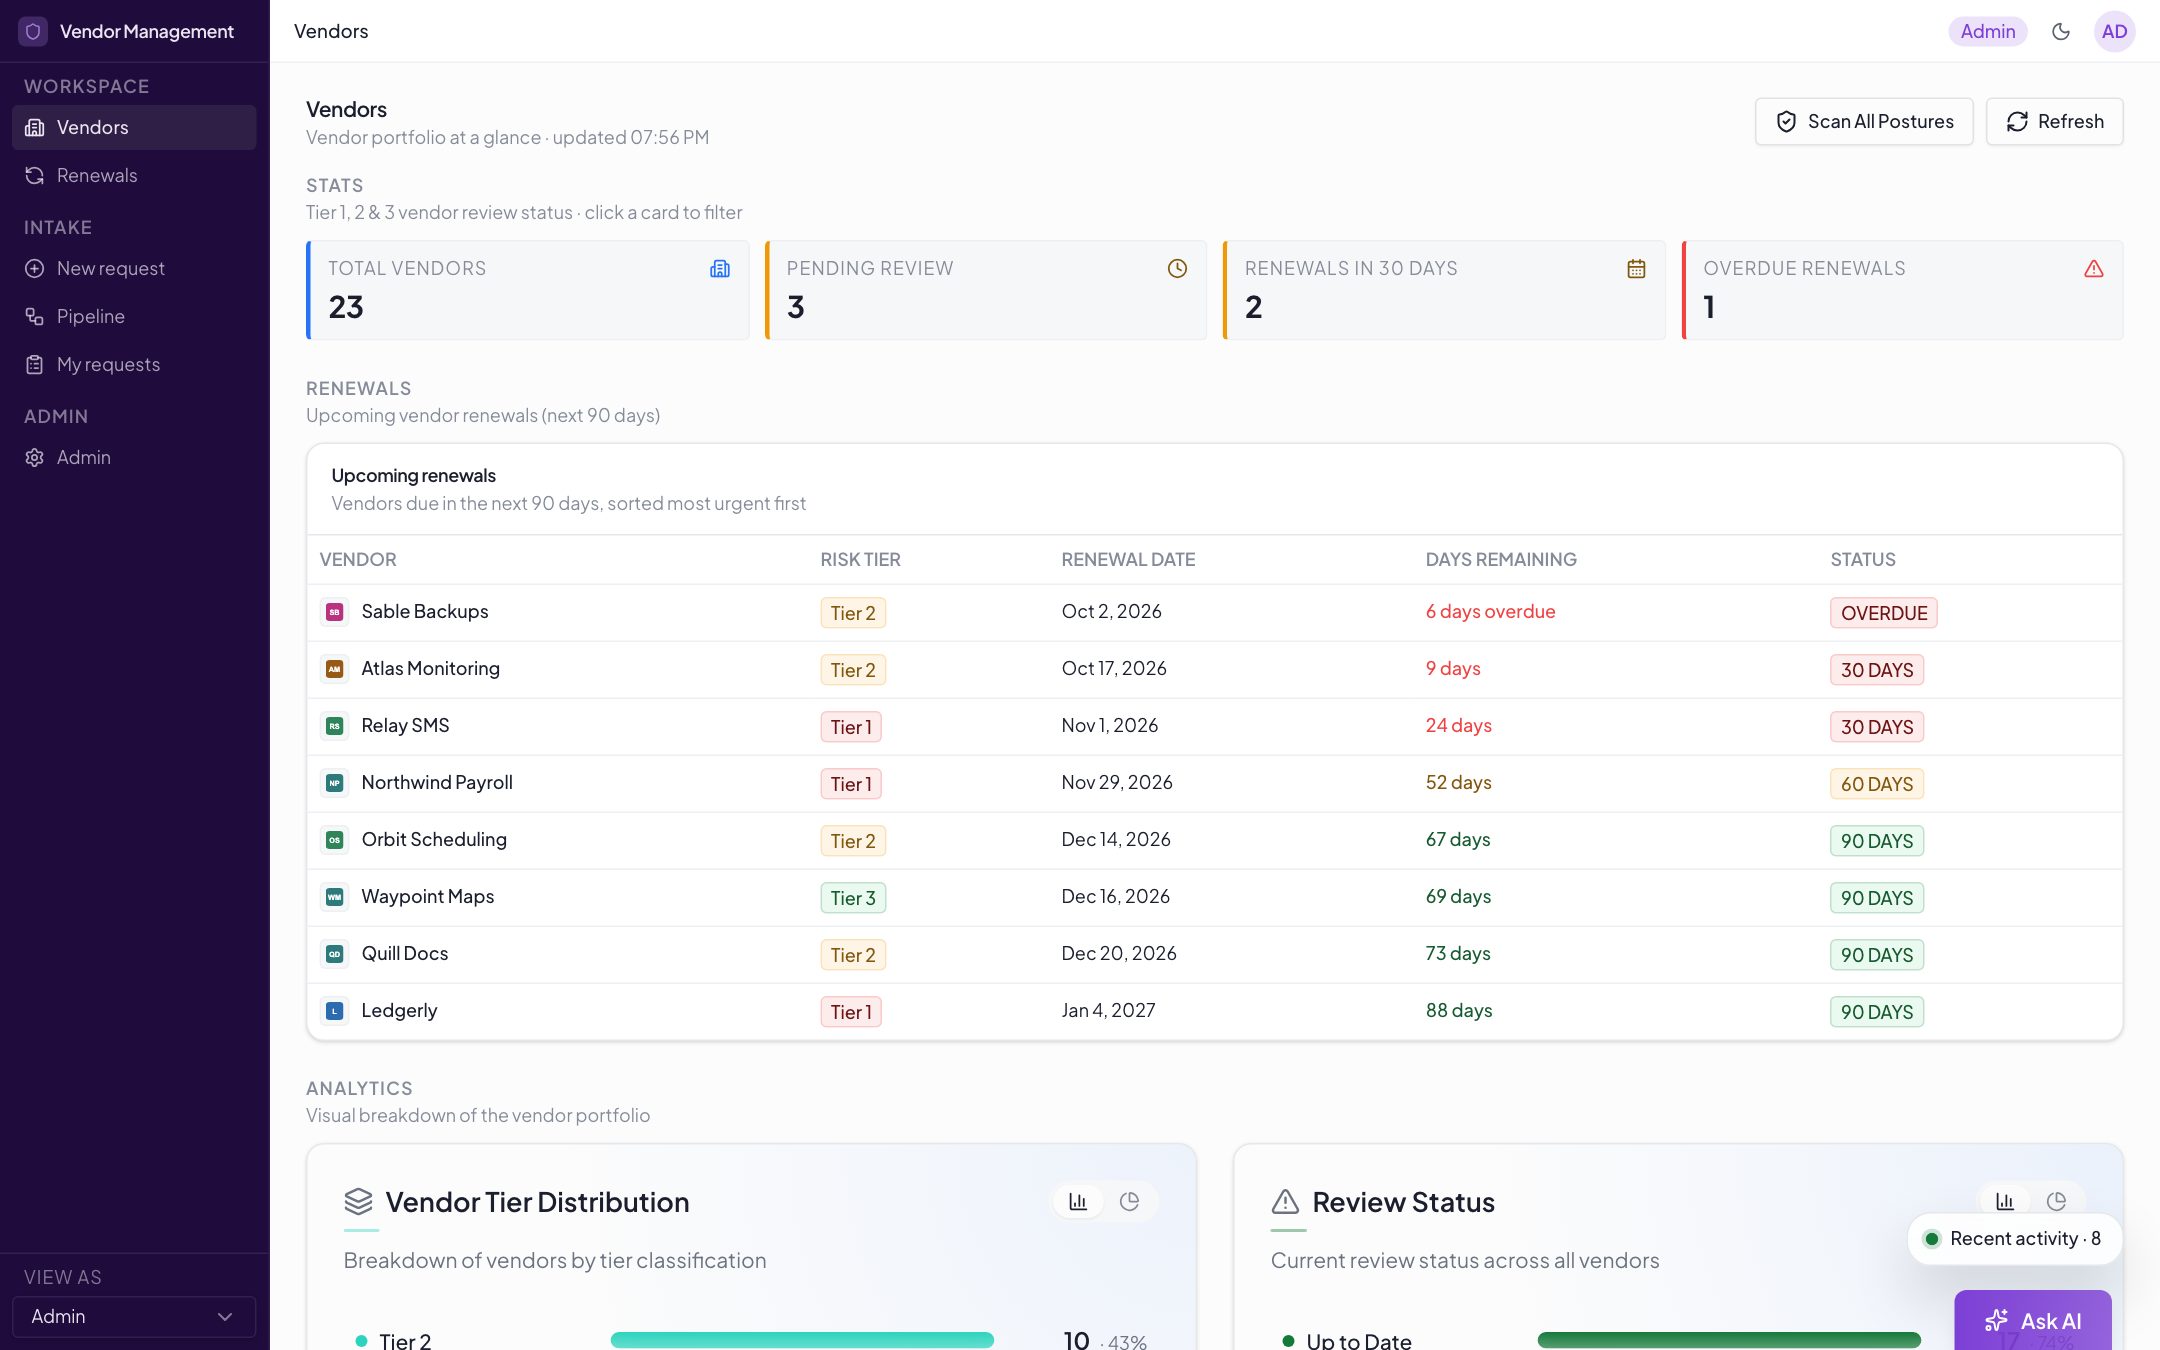
03One front doorEvery vendor request lands in one system, with an AI draft ready before review.
04Write for the readerPolicies rewritten in plain language, with a human approving every change.
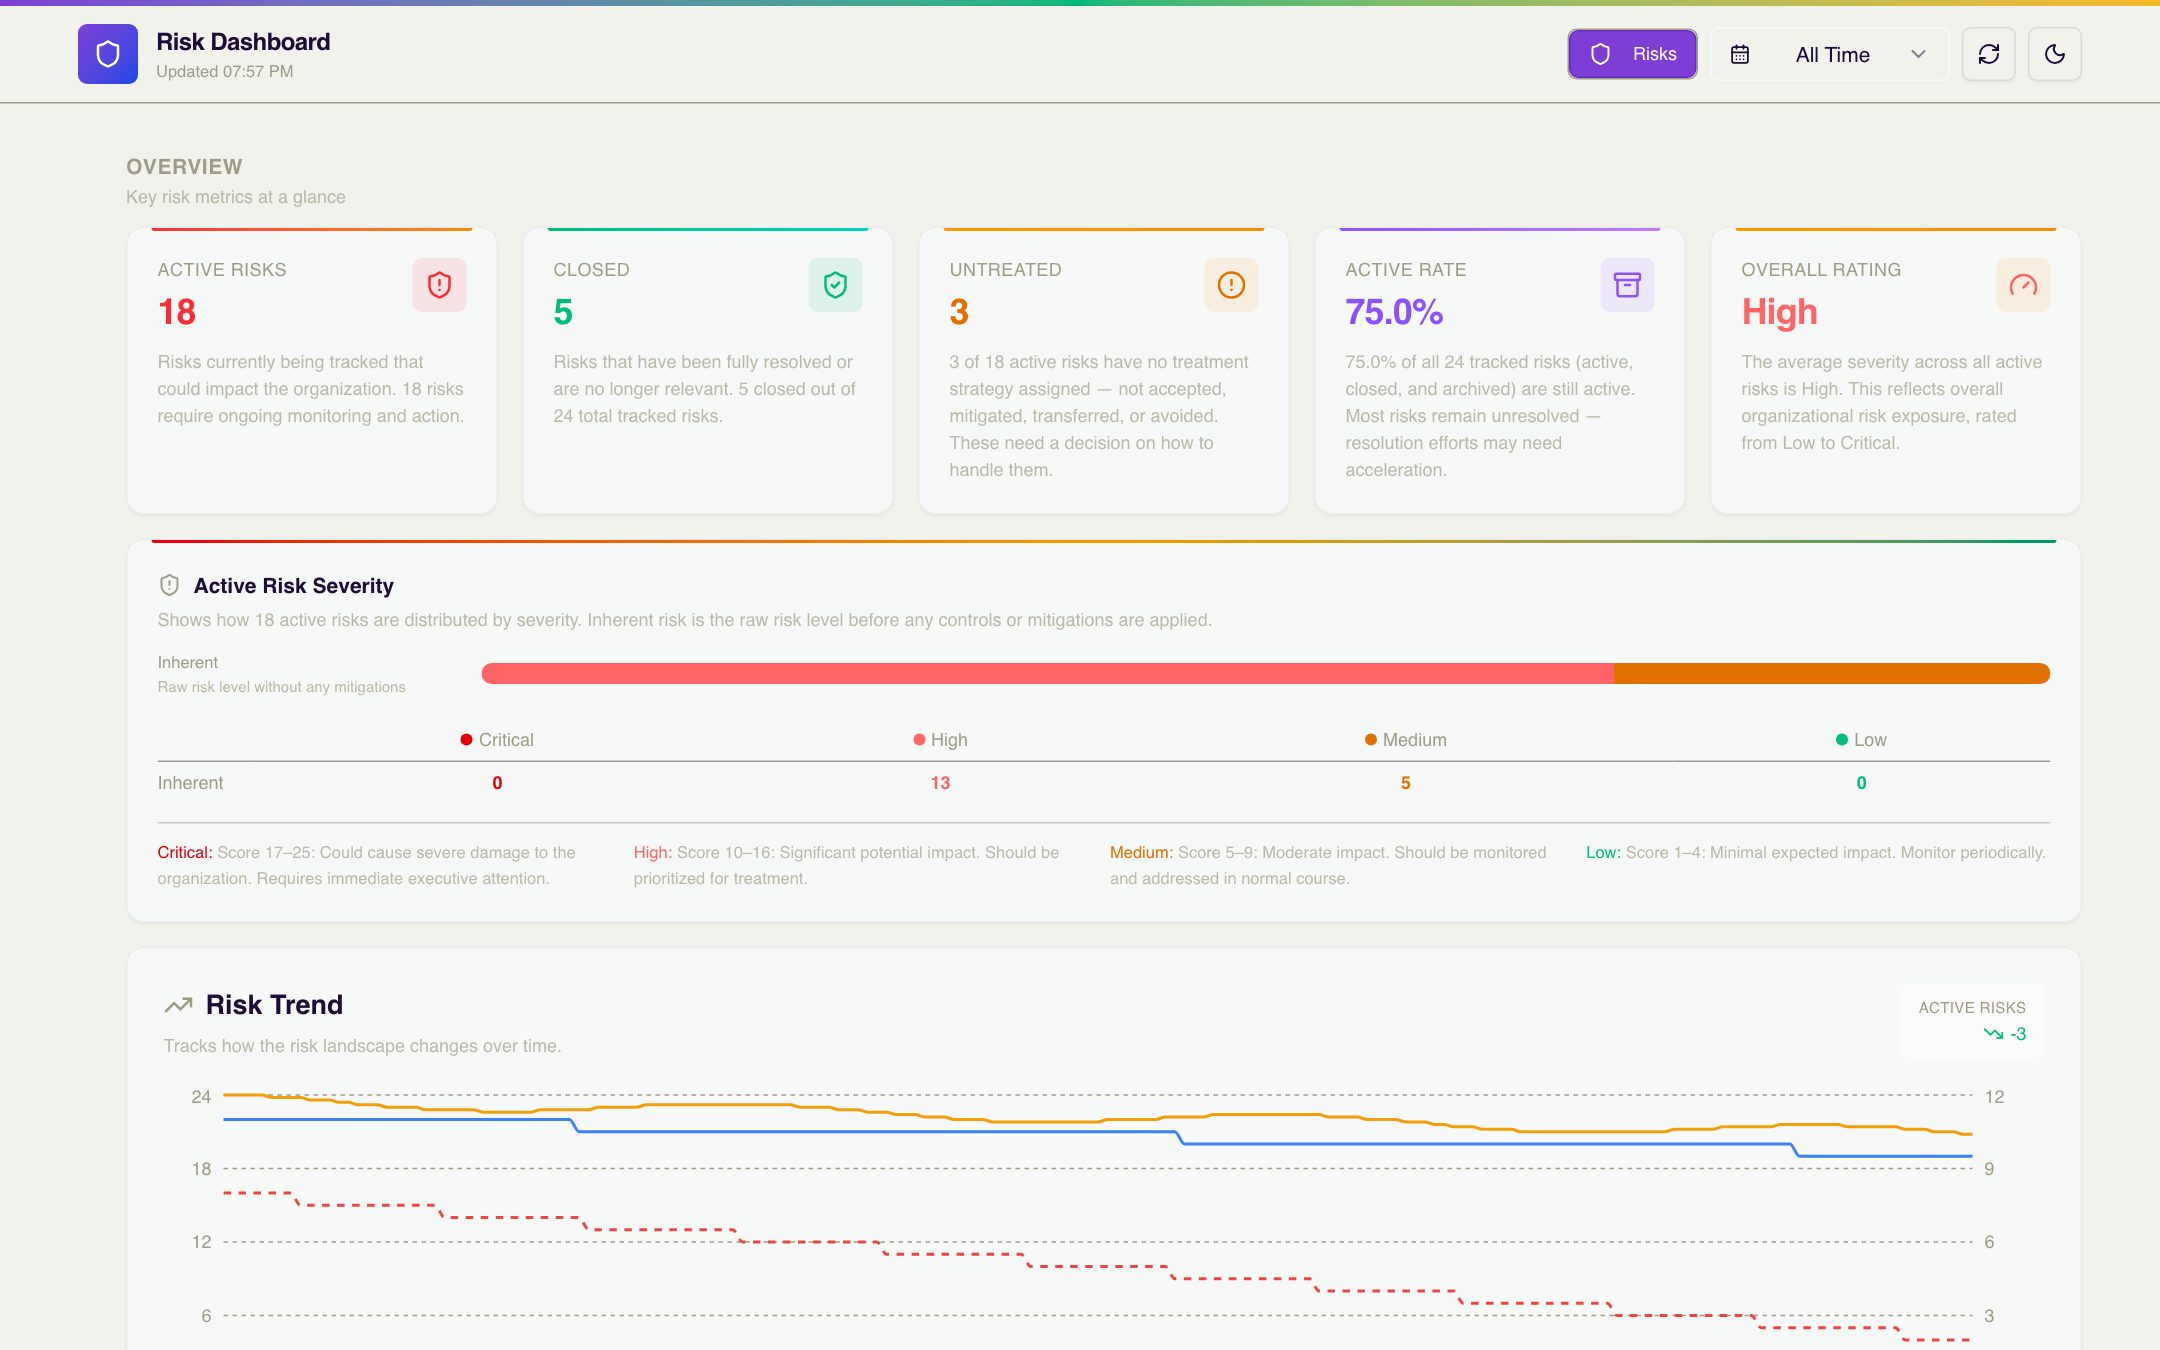
05Make risk visibleA top 10 view leadership reads in a minute and owners act on.